Canton Cybersecurity
Cyberattack on USI puts job and scholarship application data at risk
The Università della Svizzera italiana has disclosed a cyberattack that, between 9 and 17 November, exposed data held on one of its applications. The issue involves an online form system used for job applications, scholarship requests and surveys.
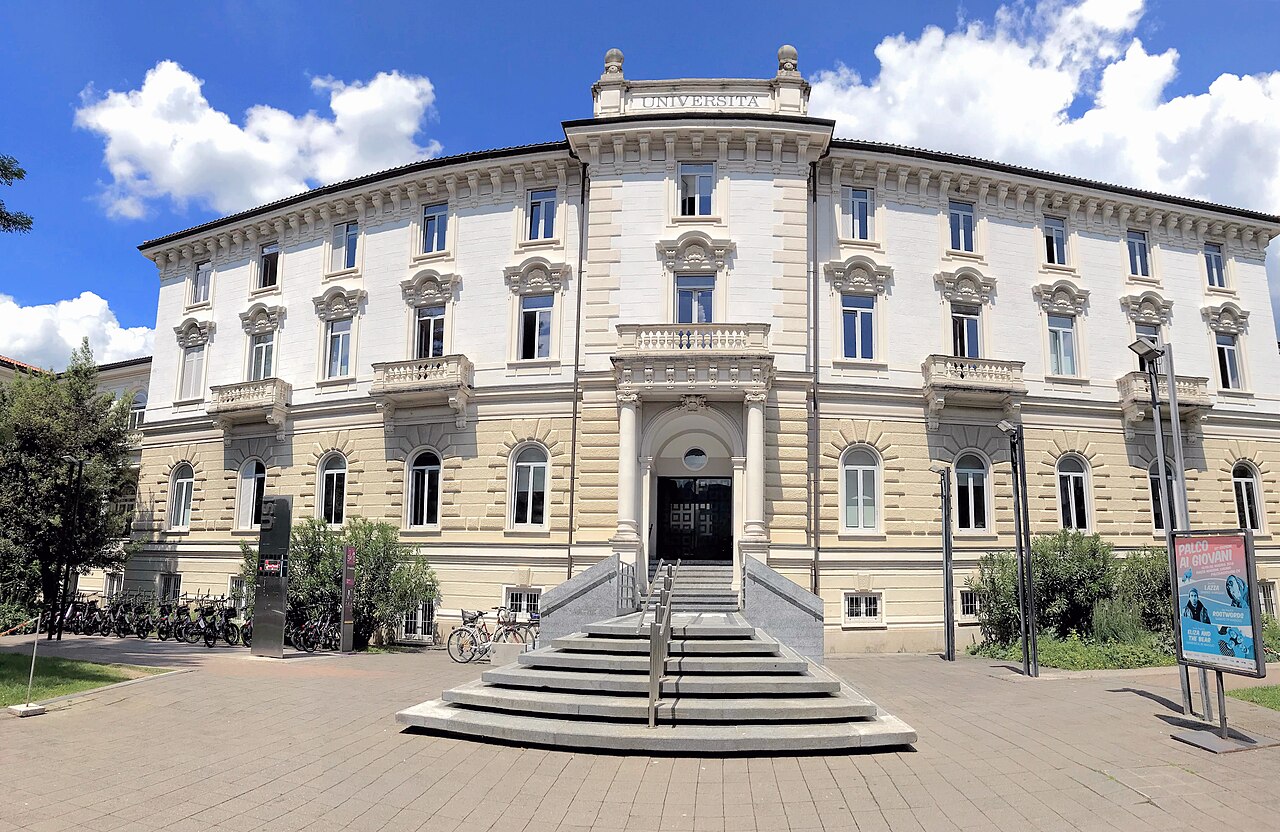
The Università della Svizzera italiana (USI), whose main campus is in Lugano, announced on Thursday 19 November that it had been the victim of a cyberattack that took place between 9 and 17 November. In its statement, the university explains that the incident allowed unauthorised third parties to access data stored on one of its IT systems.
According to the university, the attackers managed to get into the system by exploiting a flaw in the software that runs its online forms. The same tool is used, among other things, to collect job applications, requests for scholarships and survey responses. Anyone submitting a job application or a scholarship request typically provides personal data and, in some cases, financial information. It has not been specified how long the flaw had existed in the system, nor how many forms or people were affected by the intrusion.
Measures taken
The university responded on several fronts as soon as the problem was identified. Its IT department isolated the affected server, preventing further access to the data stored on it.
The university also alerted the competent authorities and individually contacted people who, having used the affected form, may have had their data exposed, so that they can assess any precautions to take.
The institution says it is working closely with the authorities and with external cybersecurity specialists to clarify the circumstances of the incident. It remains to be established exactly how the intrusion into the system was possible and how far it extended, including which data were actually accessed or taken. No timeline has been given for the conclusion of these inquiries.
Comments
There are no comments yet. Yours can be the first voice.